Securing mission-critical systems against live cyber threats.
We deploy research-grade vulnerability engines, real-time threat neutralization methodologies, and high-assurance manual source code audits across Web & API, AI Infrastructure, Android, and Open-Source software.
The Founders
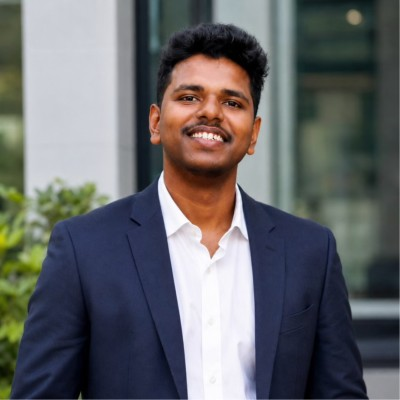
Siva Aditya Panuganti
Lead Researcher and Principal Architect at Aditya Security Labs. Specializing in advanced vulnerability research, zero-day discovery, and security architecture.
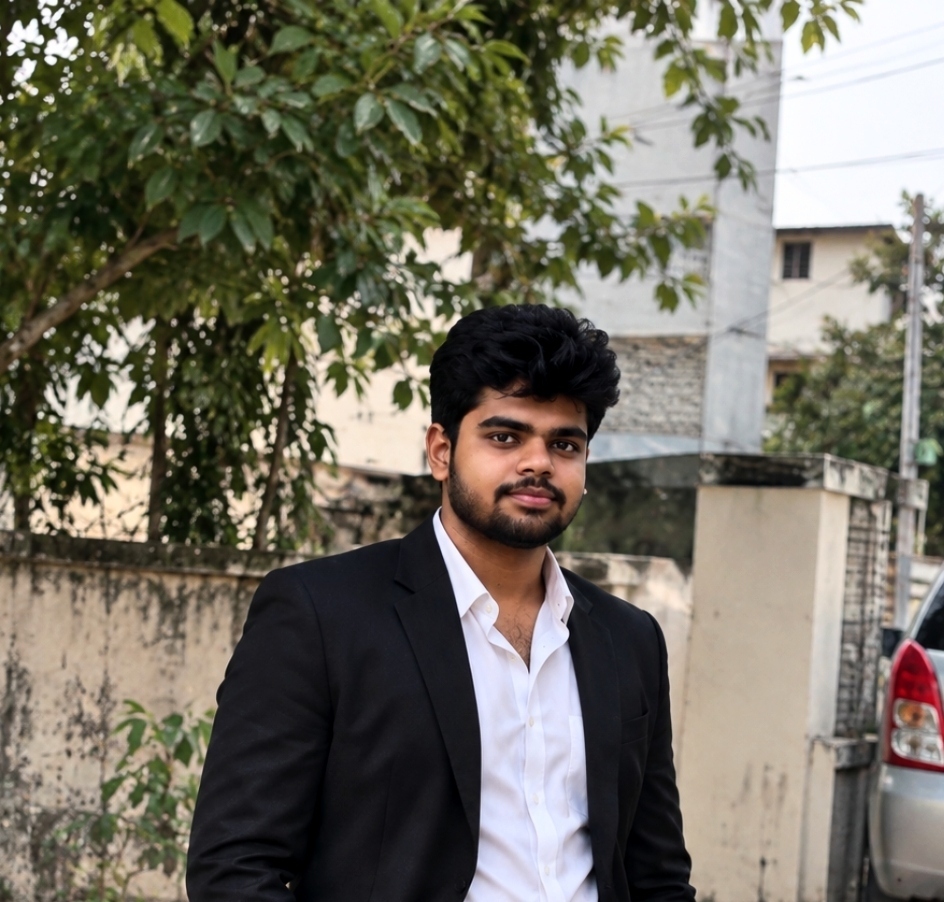
Ainavilli Swamy Ganesh
Co-Founder at Aditya Security Labs. Specializing in Android application security, defensive engineering, adversarial AI threat modeling (WormGPT-type evasion), practical fraud exposure, and blue-team SOC countermeasures.
Security Services
We deliver elite, research-driven security audits and manual vulnerability research across four core technological pillars, identifying high-impact vulnerabilities before malicious exploitation.
Web & API Security
Rigorous manual code review and adversarial penetration testing for complex web applications and modern APIs (REST, GraphQL, gRPC). We target nuanced business logic bypasses, authorization flaws (BOLA / IDOR), broken object properties, SSRF, Deserialization RCEs, and advanced SQL injection vectors with zero false positives.
AI & LLM Security
Advanced threat modeling and adversarial robustness verification for autonomous AI platforms, RAG systems, and vector databases. We discover and remediate sandbox escape vulnerabilities (e.g. Flowise CVE-2026-73484, Qdrant CVSS 9.1), runtime API key leakages (AutoGPT CVE-2026-22038), prompt injection escapes, and verify EU AI Act Article 15 compliance.
Android Security
Full-lifecycle Android application security assessments led by Co-Founder Ainavilli Swamy Ganesh. Comprehensive APK reverse engineering, Smali/Java/Kotlin decompilation, inter-process communication (IPC) and Intent exposure auditing, insecure cryptographic storage analysis, and dynamic runtime instrumentation with Frida and Objection.
OSS & Supply Chain Security
Deep vulnerability research and source code auditing for open-source repositories, critical digital infrastructure, and third-party dependencies. We verify Software Bills of Materials (SBOMs), detect upstream supply chain risks, and conduct responsible Coordinated Vulnerability Disclosures (CVD) with patch-ready pull requests and published NIST CVEs.
Core Capabilities
We deploy advanced, research-driven methodologies that go far beyond automated scanning, focusing exclusively on complex, high-impact vulnerabilities.
Recent Research
Selected CVE Research
6 Official NIST / NVD Disclosures
The following records are linked directly to their NVD pages so that the affected product, vulnerability description, references, and available severity information can be checked independently.
| CVE record | Project | Vulnerability | Official proof |
|---|---|---|---|
| CVE-2026-70383 | DigiDoc4 Client | Path traversal / arbitrary file overwrite, CWE-22 | NVD record ↗ |
| CVE-2026-73484 | Flowise | Python sandbox escape through insufficient restrictions on native Pandas methods | NVD record ↗ |
| CVE-2026-22038 | AutoGPT Platform | Plaintext logging of API keys and authentication secrets in the Stagehand integration, CWE-532 | NVD record ↗ |
| CVE-2025-68621 | Trilium Notes | Timing attack against sync authentication that could enable HMAC recovery, CWE-208 | NVD record ↗ |
| CVE-2025-67146 | GYM-MANAGEMENT-SYSTEM 1.0 | Multiple SQL injection vulnerabilities with possible data extraction, authentication bypass, and database modification | NVD record ↗ |
| CVE-2025-67147 | Gym-Management-System-PHP 1.0 | Multiple SQL injection vulnerabilities that could enable authentication bypass, data modification, deletion, and privilege escalation | NVD record ↗ |
Bespoke Advisory
Managed Assessment
Full ASL V6 scan, verified findings report, and comprehensive remediation guidance delivered directly to your engineering leadership in 5 days.
Technical Retainer
Ongoing architectural review and remediation. Vulnerability patches are written and submitted directly to your codebase as pull requests by our lead researcher.
Emergency Assessment
Expedited 1-week pre-launch code audit or immediate post-incident review accompanied by proof-of-concept exploits to verify remediation.
EU AI Act Assessment
Article 15 adversarial robustness testing for Annex III high-risk AI — legal tech, medical AI, biometric analysis, and autonomous systems.
How It Works
Request Audit
Fill out the audit request. We respond within 24 hours with an NDA to secure your intellectual property.
Engine & Manual Review
We run the ASL V6 Engine and a rigorous manual review against your codebase. Typically completed in 3–5 business days.
Patch-Ready Findings
You receive a verified findings report with patch-ready fixes, eliminating ambiguity for your engineering team.
Request Audit.
All engagements begin with a confidential consultation to understand your application architecture, technology stack, and security objectives. Strict NDA provided before any code access.
Common Questions
Can you audit codebases outside Python?
Yes. While ASL V6 specializes in Python and AI agents, our manual methodology covers Android mobile apps (Kotlin/Java), Node.js, and web stacks.
Do you require source code access?
Yes, for Managed Assessments and Retainers. Emergency Assessments can begin with a running application.
What is your payment structure?
50% upfront, 50% on delivery for fixed-price engagements. Retainers are billed monthly.
Do you work with early-stage startups?
Yes. We offer a reduced-scope assessment for seed-stage teams. Mention your funding stage in the request.